Static code analysis tools can help teams find defects, security risks, and code-quality issues without running a program, but these eight listings are books and guides about the tools rather than software products themselves. I rank Static Analysis Engineering as the best overall starting point for its focus on finding defects before production, while Secure Programming with Static Analysis stands out for security-minded readers and The Cobra Static Code Analyzer: User Guide for readers seeking tool-specific direction. The main tradeoff is between practical guidance, security coverage, and deeper technical or academic treatment. Several entries are specialized, dated, or limited by language or format, so the right choice depends on what you need to learn. Read on for the full comparison and help matching each guide to your goals.

Get business pricing on monitors, keyboards and dev gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Key Takeaways
- Static Analysis Engineering ranks first because defect detection before production gives it the broadest practical fit among these titles.
- Secure Programming with Static Analysis is the clearest match for security-focused learning; it has a narrower purpose than a general engineering guide.
- The Cobra Static Code Analyzer: User Guide is tool-specific, which can help Cobra users but limits its usefulness as a general reference.
- Program Analysis and Optimization in Static Compilers offers the most technically specialized scope, including flow analysis and symbolic execution, and is less suited to readers seeking an introductory manual.
- The lineup consists of books and guides, not deployable analyzers; the 2020 edition and German-language title also call for checks on currency and language fit.
| The Cobra Static Code Analyzer: User Guide |  | Best for Cobra Users | Resource type: User guide | Named tool: Cobra static code analyzer | Subject: Using a static code analyzer | VIEW LATEST PRICE | See Our Full Breakdown |
| Secure Programming with Static Analysis |  | Best for Secure Coding | Format: Book | Subject: Secure programming | Primary method: Static analysis | VIEW LATEST PRICE | See Our Full Breakdown |
| Program Analysis and Optimization in Static Compilers: Flow Analysis, Symbolic Execution, and Performance Diagnostics |  | Best for Compiler Specialists | Resource type: Book | Subject: Program analysis and optimization | Application area: Static compilers | VIEW LATEST PRICE | See Our Full Breakdown |
| Static Program Analysis Techniques: Ensuring High-Quality Code |  | Best Broad Reference | Resource type: Book | Subject: Static program analysis | Stated goal: High-quality code | VIEW LATEST PRICE | See Our Full Breakdown |
| Static Analysis Engineering: Detecting Software Defects Before They Reach Production |  | Best for Defect-Prevention Focus | Resource type: Not specified | Subject: Static analysis engineering | Stated goal: Detect software defects before production | VIEW LATEST PRICE | See Our Full Breakdown |
| Comparison of Fagan Inspections and Tool-Supported Static Code Analysis (German Edition) |  | Best for Comparing Review Methods | Language: German | Subject: Software engineering | Focus: Comparison of Fagan inspections and tool-supported static code analysis | VIEW LATEST PRICE | See Our Full Breakdown |
| Open Source Static Code Analysis Tool: A Complete Guide (2020 Edition) | 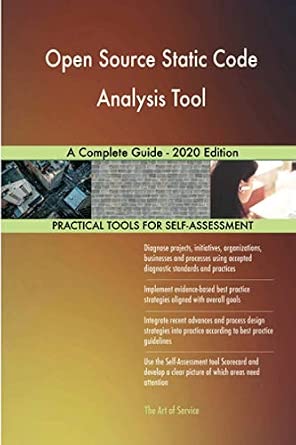 | Best for Open-Source Tool Orientation | Edition: 2020 | Subject: Static code analysis | Tool focus: Open-source tools | VIEW LATEST PRICE | See Our Full Breakdown |
| Static Code Analysis for Security – Comparison of Software Packages |  | Best for Security-Focused Comparisons | Subject: Static code analysis for security | Work type: Comparison of software packages | Evaluation focus: Features and effectiveness | VIEW LATEST PRICE | See Our Full Breakdown |
| static code analysis tool | Subject | Resource type | Format | ASIN |
|---|---|---|---|---|
| The Cobra Static Code Analyzer | Using a static code analyzer | User guide | Not specified | — |
| Secure Programming with Static | Secure programming | — | Book | 0321424778 |
| Program Analysis and Optimizat | Program analysis and optimization | Book | — | — |
| Static Program Analysis Techni | Static program analysis | Book | — | — |
| Static Analysis Engineering: D | Static analysis engineering | Not specified | — | — |
| Comparison of Fagan Inspection | Software engineering | — | Book | 3656340668 |
| Open Source Static Code Analys | Static code analysis | — | Guide | 0655942386 |
| Static Code Analysis for Secur | Static code analysis for security | — | — | B005JMXIE4 |
More Details on Our Top Picks
The Cobra Static Code Analyzer: User Guide
The Cobra Static Code Analyzer: User Guide is the most tool-specific choice in this group: its stated focus is helping readers use Cobra, rather than teaching static analysis broadly. That makes it a more direct fit for someone who has already selected Cobra than Static Program Analysis Techniques: Ensuring High-Quality Code, which presents a wider view of methods, tools, and case studies. The tradeoff is that the available description gives no detail about supported languages, setup steps, rule coverage, or how current the guidance is. I would treat this as a companion reference, not evidence that Cobra itself suits a particular codebase. Readers seeking security-analysis principles across tools may get more from Secure Programming with Static Analysis; readers who need Cobra-specific help should start here, while verifying the guide matches their software version.
Pros:- Focuses specifically on the Cobra static code analyzer
- Can serve as a focused companion for readers working with Cobra
- Keeps attention on using an analyzer rather than general software engineering
Cons:- No details are provided about languages, installation, rules, or workflow
- The available information does not establish whether its guidance matches current Cobra versions
- Its tool-specific scope offers less breadth than general static analysis books
Best for: Developers or teams already evaluating or using Cobra who need a guide focused on that analyzer.
Not ideal for: Readers choosing among static analysis tools or seeking broad security guidance, since the supplied details do not describe comparative coverage or general methods.
- Resource type:User guide
- Named tool:Cobra static code analyzer
- Subject:Using a static code analyzer
- Format:Not specified
- Language coverage:Not specified
- Publication date:Not specified
Our verdict“Choose this guide if Cobra is already your intended analyzer; pick a broader reference if you are still comparing tools or learning static analysis fundamentals.”
Secure Programming with Static Analysis
Secure Programming with Static Analysis is the clearest match for developers whose main reason to add static analysis is finding security weaknesses before code ships. Its security-centered scope gives it a different purpose from Static Program Analysis Techniques: Ensuring High-Quality Code, which addresses broader quality concerns, and from the Cobra guide, which is tied to one named analyzer. That focus can help readers connect analysis to safer programming practices rather than treating findings as a generic warning list. The supplied information, however, does not identify specific tools, languages, examples, or whether the guidance reflects current development workflows. I would choose it for a security-first learning goal, not as a tool-selection manual or a complete account of testing. Buyers seeking compiler theory will find Program Analysis and Optimization in Static Compilers more technically specialized.
Pros:- Centers static analysis on secure software development
- Provides a focused alternative to general code-quality references
- Book format suits readers seeking a sustained learning resource
Cons:- The supplied description names no specific analyzers or supported languages
- No details are provided about examples, exercises, or current tool workflows
- Security focus does not cover the full range of static analysis and testing needs
Best for: Software developers, secure-coding learners, and application security practitioners who want to understand static analysis as part of preventing software vulnerabilities.
Not ideal for: Readers who need a current tool comparison, language-specific setup instructions, or detailed compiler optimization coverage.
- Format:Book
- Subject:Secure programming
- Primary method:Static analysis
- Stated focus:Writing secure software
- Specific tools listed:Not specified
- Language coverage:Not specified
- ASIN:0321424778
Our verdict“Pick this book when secure coding is your primary goal, but look elsewhere for tool-by-tool selection advice or compiler-focused analysis.”
Program Analysis and Optimization in Static Compilers: Flow Analysis, Symbolic Execution, and Performance Diagnostics
Program Analysis and Optimization in Static Compilers is the most technically specialized option here, with stated coverage of flow analysis, symbolic execution, and performance diagnostics. Those topics make it a stronger match for compiler engineers and advanced students than Static Analysis Engineering: Detecting Software Defects Before They Reach Production, whose description emphasizes defect prevention without specifying comparable compiler methods. Its practical examples are useful because they connect theory to performance diagnosis, while the theoretical foundation can help readers reason about how analyses work beneath tool interfaces. The main cost is accessibility: the description explicitly warns that the material may challenge beginners. It also centers compiler efficiency and optimization, not just routine bug or security detection. For a broader quality-focused introduction, Static Program Analysis Techniques: Ensuring High-Quality Code is likely a closer fit.
Pros:- Covers flow analysis and symbolic execution
- Includes performance diagnostics in a compiler context
- Combines theoretical foundations with practical approaches
- Practical examples connect analysis methods to compiler efficiency
Cons:- Highly technical material may be difficult for beginners
- Compiler optimization focus is narrower than general static code quality
- The supplied details do not identify languages, tools, or specific case studies
Best for: Compiler developers, graduate-level students, and experienced engineers studying flow analysis, symbolic execution, or static compiler performance.
Not ideal for: Beginners seeking a gentle introduction or application developers mainly looking for practical defect and security checks in everyday projects.
- Resource type:Book
- Subject:Program analysis and optimization
- Application area:Static compilers
- Named technique:Flow analysis
- Named technique:Symbolic execution
- Named topic:Performance diagnostics
- Approach:Theoretical foundations and practical methods
Our verdict“Choose this book for advanced compiler analysis and optimization study, not as a beginner’s guide to choosing a general-purpose code checker.”
Static Program Analysis Techniques: Ensuring High-Quality Code
Static Program Analysis Techniques: Ensuring High-Quality Code takes the broadest practical quality angle in this set: its description spans analysis methods, tools, and real-world case studies aimed at finding bugs early and improving maintainability. That makes it a more general starting point than Secure Programming with Static Analysis, which centers security, and less specialized than Program Analysis and Optimization in Static Compilers, which focuses on compiler techniques. The stated tool recommendations and examples may help students and working developers connect concepts to code-review workflows. Its scope still has limits: it does not cover dynamic testing, and absolute beginners may find the technical material difficult. The supplied information also does not name specific tools or languages, so readers needing an implementation guide should not assume it offers setup instructions for their stack.
Pros:- Covers multiple static program analysis methods
- Includes practical examples and tool recommendations
- Connects early defect detection with maintainability
- Uses real-world case studies according to the description
Cons:- May be too technical for absolute beginners
- Does not cover dynamic testing methods
- No specific tools or programming languages are named in the supplied details
Best for: Students and professional developers who want a broad introduction to static analysis methods, code-quality goals, and practical tool use.
Not ideal for: Absolute beginners who need an entry-level explanation, or teams seeking dynamic testing guidance and language-specific setup steps.
- Resource type:Book
- Subject:Static program analysis
- Stated goal:High-quality code
- Coverage:Theory and practical tools
- Examples:Practical examples
- Case studies:Real-world case studies
- Additional testing coverage:Dynamic testing not covered
Our verdict“Choose this as a broad static-analysis reference for code quality, while pairing it with other resources for dynamic testing or security-only depth.”
Static Analysis Engineering: Detecting Software Defects Before They Reach Production
Static Analysis Engineering: Detecting Software Defects Before They Reach Production is framed around the engineering goal of catching defects before release, making it appealing to teams that want analysis embedded in their quality process. Compared with Static Program Analysis Techniques: Ensuring High-Quality Code, this title signals a narrower emphasis on defect prevention rather than a stated mix of theory, tools, and case studies. That positioning may suit readers who care about when analysis enters the development lifecycle, but the available description supplies no details about methods, integrations, languages, or examples. I would not treat the title alone as proof of a practical implementation playbook. Readers who need named analysis techniques have firmer detail in Program Analysis and Optimization in Static Compilers; those prioritizing security have a clearer subject match in Secure Programming with Static Analysis.
Pros:- Explicitly frames static analysis around pre-production defect detection
- Its engineering focus may appeal to teams thinking about development workflow
- Title makes the intended quality goal clear
Cons:- No specific analysis techniques or tools are described
- No details are provided about examples, languages, or workflow integration
- The limited product information makes its depth and audience difficult to judge
Best for: Engineering leads and developers looking for a resource framed around preventing software defects before production, provided they can verify its actual coverage.
Not ideal for: Readers who need confirmed language support, tool recommendations, implementation steps, or a clearly documented security-analysis curriculum.
- Resource type:Not specified
- Subject:Static analysis engineering
- Stated goal:Detect software defects before production
- Specific techniques:Not specified
- Tools covered:Not specified
- Language coverage:Not specified
- Publication date:Not specified
Our verdict“Consider this only if its defect-prevention focus matches your goal and you can confirm the contents meet your team’s practical needs.”
Comparison of Fagan Inspections and Tool-Supported Static Code Analysis (German Edition)
This German-language work takes a comparative angle that most tool-focused guides do not: it sets Fagan inspections alongside tool-supported static analysis. That makes it a useful choice for readers deciding how human review and automated checks might fit into a software quality process, rather than looking for a setup manual. Compared with Open Source Static Code Analysis Tool: A Complete Guide (2020 Edition), its stated focus is the contrast between methods, not an overview of open-source tools. The tradeoff is limited visibility: no description or further details are supplied, so I cannot verify its depth, examples, or practical recommendations. Its German language also narrows its audience. I would rank it for process comparison, but choose a security-focused comparison or a hands-on guide for tool selection and implementation.
Pros:- Directly compares Fagan inspections with tool-supported static code analysis
- Addresses software engineering process choices, not only tool features
- Written in German for readers who prefer German-language technical material
Cons:- No description or additional details are provided to judge scope, examples, or depth
- German-language content limits usefulness for readers who need an English reference
- The available information does not establish tool coverage or how current the comparison is
Best for: German-reading software engineering students, instructors, and development leads comparing formal inspections with automated static-analysis practices
Not ideal for: Readers who need current tool recommendations, implementation steps, or an English-language reference; the available details do not establish that it covers these needs
- Language:German
- Subject:Software engineering
- Focus:Comparison of Fagan inspections and tool-supported static code analysis
- Format:Book
- Edition:German Edition
- ASIN:3656340668
Our verdict“Choose this if you read German and want to compare human inspection with automated analysis, but not if you need a verified, practical tool-selection guide.”
Open Source Static Code Analysis Tool: A Complete Guide (2020 Edition)
The title points to a guide for readers surveying open-source static analysis tools, making this the most directly targeted starting point here for that category. Its 2020 edition label gives buyers a date to weigh: it may help frame tool choices, but the supplied details do not confirm which projects, languages, or workflows it covers. Compared with Static Code Analysis for Security – Comparison of Software Packages, this guide is explicitly open-source-oriented, while the other title emphasizes security comparisons. That distinction helps narrow the choice, but not the content depth. No description or technical specifications beyond the edition are provided, so I would not rely on it alone for present-day implementation decisions. It suits a reader seeking orientation; readers wanting a documented security evaluation or concrete setup instructions should verify the contents first.
Pros:- Explicitly focuses on open-source static code analysis tools
- A guide format is suited to readers seeking a broad introduction
- The 2020 edition label gives readers a clear point of reference for its publication period
Cons:- No description is provided to confirm the tools, languages, or topics covered
- The 2020 edition may not reflect later changes in open-source tools
- Available details do not confirm practical setup advice or comparative evaluation criteria
Best for: Developers, students, or engineering teams beginning a survey of open-source static-analysis options and comfortable checking tool details against current sources
Not ideal for: Teams choosing a current production tool or seeking confirmed language coverage, installation guidance, or security evaluation; none of those details are supplied
- Edition:2020
- Subject:Static code analysis
- Tool focus:Open-source tools
- Format:Guide
- Language:Not specified
- ASIN:0655942386
Our verdict“Pick this as an initial open-source tool survey if you will verify its coverage and recency before making a tooling decision.”
Static Code Analysis for Security – Comparison of Software Packages
This is the most clearly security-centered option in the batch: its stated scope compares static-analysis software packages by features, effectiveness, and suitability for different development environments. That framing can help security-minded buyers think beyond a feature checklist and ask whether a package fits their workflow. Compared with Open Source Static Code Analysis Tool: A Complete Guide (2020 Edition), it is defined by vulnerability detection rather than open-source coverage. The limitation is that no named tools, test methods, supported languages, or publication details are provided, so the promised comparison cannot be evaluated from the available information. I would favor it over a general tool survey only when security is the main selection criterion and the full work confirms its evidence and scope; buyers seeking implementation instructions may prefer a dedicated user guide such as The Cobra Static Code Analyzer: User Guide.
Pros:- Centers its comparison on security vulnerabilities
- States that it evaluates features and effectiveness, not just package names
- Considers suitability across development environments
Cons:- No specific software packages or supported languages are identified in the available details
- Evaluation methods and evidence for effectiveness are not described
- No publication date or implementation guidance is provided
Best for: Application-security leads and developers comparing static-analysis packages specifically for vulnerability detection across development environments
Not ideal for: Buyers who need verified tool names, benchmark methods, language support, or step-by-step configuration guidance; those details are not supplied
- Subject:Static code analysis for security
- Work type:Comparison of software packages
- Evaluation focus:Features and effectiveness
- Use case:Security vulnerability analysis
- Development environments:Suitability across various environments
- Language:Not specified
- Publication date:Not specified
- ASIN:B005JMXIE4
Our verdict“Choose this for a security-first package comparison if the full text confirms its tools and evaluation methods; otherwise, use it only as a lead for further research.”
How We Picked
I evaluated these entries as learning resources about static analysis, not as software packages that can scan a repository. I compared each title by its stated focus, how directly that focus supports a reader’s goal, its apparent practical or technical orientation, and how broad a range of readers it may serve. I also considered limits signaled by the listing, including tool-specific scope, specialist subject matter, language, and publication edition.
The ranking favors clear practical relevance and broad usefulness first, then rewards focused security guidance or a distinctive technical subject for readers with those needs. Titles with narrower audiences rank lower as general recommendations, even when their specialized scope may be valuable to the right reader. Since these are publications rather than runnable tools, this roundup cannot compare detection accuracy, IDE integration, language support, or scan performance; buyers should confirm those details from the publication itself before choosing.
| static code analysis tool | Resource type | Format |
|---|---|---|
| The Cobra Static Code Analyzer | User guide | Not specified |
| Secure Programming with Static | — | Book |
| Program Analysis and Optimizat | Book | — |
| Static Program Analysis Techni | Book | — |
| Static Analysis Engineering: D | Not specified | — |
| Comparison of Fagan Inspection | — | Book |
| Open Source Static Code Analys | — | Guide |
| Static Code Analysis for Secur | — | — |
Factors to Consider When Choosing Static Code Analysis Tools
These listings can build understanding of static analysis, but they cannot replace selecting and trialing an analyzer for your codebase. I would first decide whether I need an implementation guide, a security-focused reference, technical theory, or a tool-specific manual. Then I would check whether the publication is current and whether its examples match my languages and team workflow.
Start With the Learning Goal, Not the Tool Name
Separate learning about analysis from adopting an analyzer. A user guide can explain one named tool, while a general engineering text may help readers reason about defect-finding practices across tools. Buying a tool-specific guide before confirming that your team uses that tool can leave you with little reusable material. Conversely, broad theory may not tell a new user how to configure a real scan. Match the title’s scope to the next decision you need to make, such as choosing a tool, understanding findings, or planning team adoption.
Check Language and Version Fit
Static analyzers change as languages, frameworks, and security rules evolve, so publication date and edition can affect how useful examples are. The listing explicitly identifies a 2020 edition for one guide; check whether its advice still matches current tool versions and development practices. Also confirm the language of the text: the Fagan inspections comparison is identified as a German edition. Do not assume a title’s broad wording means its examples cover your programming language or framework. If you need current setup steps, verify the contents and edition details before treating any book as an operational manual.
Distinguish Security Analysis From General Quality Checks
Security-focused analysis usually asks different questions from general defect or maintainability checks. A resource centered on secure programming may help teams think about vulnerabilities, while a general static-analysis guide may address a wider set of defects. Teams often make the mistake of assuming one perspective covers the other automatically. Define the risks that matter to your project, then check whether the publication addresses those risks and the analysis methods you plan to use. For a software purchase, independently verify rule coverage and supported languages rather than inferring them from a book title.
Choose the Right Technical Depth
Technical depth is useful only when it serves the reader’s task. A treatment of flow analysis, symbolic execution, and performance diagnostics may suit compiler or program-analysis learners, but it can be a poor first step for someone seeking a straightforward workflow. An introductory guide can be easier to apply while offering less detail about underlying methods. Before choosing, check the contents, sample pages, and assumed background. Pay for deeper theory when your work requires understanding analysis methods or building tooling; otherwise, practical examples may be the more useful fit.
Think Beyond Detection: Workflow and Human Review
A static analyzer’s findings still need triage, ownership, and follow-up, and a guide focused on tools may not fully address those team practices. The title comparing Fagan inspections with tool-supported analysis signals a separate question: which findings benefit from human review alongside automation? Avoid treating automated checks as a complete substitute for code review or design discussion. Look for guidance that fits how your team handles false positives, prioritizes issues, and prevents repeated defects. This perspective matters even when the immediate goal is simply to learn a particular analysis technique.
Separate Learning Resources From Software Evaluation
None of these titles, by itself, proves that a software analyzer will fit your repository. When selecting an actual product, assess language and framework support, editor and build-system integration, scan time, reporting, and how teams can tune rules. Trial it against representative code, including known defects, before relying on its results. A book can help you understand the concepts or compare approaches, but it cannot establish detection quality for your project. Keep the two decisions distinct: choose a learning resource for knowledge, and evaluate software against your code and workflow.
Frequently Asked Questions
Are these listings static code analysis software I can install?
No. The eight entries are books, guides, or comparisons about static analysis rather than runnable scanning tools. They can help readers understand techniques, security concerns, or a named analyzer, but they do not scan code or integrate with a development pipeline. If your immediate need is a working analyzer, shortlist software separately and check its supported languages and workflow integrations. Use these publications as learning resources, not substitutes for a product trial.
Which title should a team read before adopting an analyzer?
Static Analysis Engineering is the broadest starting point in this lineup because its stated focus is detecting defects before production. A team choosing specifically for security may get more relevant direction from Secure Programming with Static Analysis. Before assigning either title, identify whether the team needs a shared overview, security guidance, or instructions for a particular product. Then review the contents to confirm that the material covers the languages and practices the team uses. A reading choice can support adoption, but it does not validate an analyzer’s results on your code.
Is the Cobra user guide useful if my team uses a different analyzer?
Its value is likely greatest for readers working with Cobra, since a user guide is tied to a specific analyzer. Some concepts may carry over to other tools, but the listing alone does not show how much of its instruction is general. If your team uses another product, compare the guide’s contents with that product’s documentation before buying. A broader engineering or security reference may travel better across tools. Choose the Cobra guide when tool-specific help is the goal, not as a general manual for every analyzer.
Should I choose a technical book or an introductory guide?
Choose based on what you need to do next and the background you already have. The compiler-analysis title names advanced topics such as flow analysis and symbolic execution, making it a stronger match for readers studying analysis methods than for teams looking for a quick adoption checklist. A more practical guide may be easier to apply, though it may provide less theoretical depth. Check sample material and the stated prerequisites before deciding. The best fit is the level that helps you answer a real project question without burying it in material you do not need.
Does the 2020 edition or German edition rule out a title?
Not automatically, but both are reasons to verify fit before choosing. The open-source guide is labeled as a 2020 edition, so confirm whether its examples and tool references remain relevant to your current environment. The Fagan inspections comparison is explicitly a German edition, which may be a barrier if you need English-language material. Check the publication details, contents, and sample pages rather than relying on a title alone. These limits matter most when you need current setup instructions or need the whole team to use the same resource.
Conclusion
For a broad practical starting point, I recommend Static Analysis Engineering as the best overall pick. The best value for readers seeking reusable fundamentals is Static Program Analysis Techniques: Ensuring High-Quality Code, though its exact level and coverage should be checked against the contents. For a premium, deeper technical study, choose Program Analysis and Optimization in Static Compilers; for beginners, start with the accessible scope of The Cobra Static Code Analyzer: User Guide only if Cobra is the tool in use. For specific needs, select Secure Programming with Static Analysis for security, the German Fagan comparison for readers comfortable with German and interested in inspection methods, or the open-source guide after checking its 2020 edition. If you need software rather than a book, treat these as background reading and evaluate actual analyzers on your own codebase.
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.